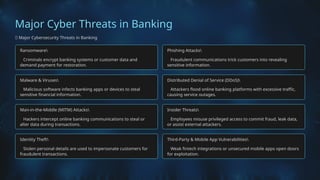
The present proposal focuses on technical safety tasks and controls with administrative nature are out of scope. The model also abstracts away future actions or suggested duties for alternative remedy including threat retention, avoidance, and sharing options. Ransomware is utilized by cybercriminals to encrypt essential knowledge and keep its house owners from having entry to it until they pay ransom. This cyberattack is a critical risk to banks; unfortunately, 90% of them have already been hit. Id and entry administration (IAM) is a cybersecurity self-discipline that offers with consumer entry and useful resource permissions.
Redefining Resilience From It Recovery To Managed Degradation
Examples of risk types are laid out in Desk 4 grouped by environment as impressed by previous research 25, 39, 57, 58 and every indexed with an distinctive identifier. The identifiers are then used for mapping security features and relevant vulnerabilities within the coming sections. Expert in IT danger management, IT project management, system databases, cybersecurity, information center enterprise options, IT infrastructure, network firewalls, routing, switching, varied system working techniques, and API options. The proposed technique is a methodical framework that includes all steps of detecting dangers from a complete viewpoint.
- Not Like other cyber attacks, a DDoS attack doesn’t try to compromise safety.
- Entry this Gartner guide to learn how to handle the entire AI inventory and safe your AI workloads with guardrails.
- Additional particulars could be added to the predefined therapy activities, significantly with suggestions for methodologies that incorporate current danger transfer and acceptance practices.
- To achieve this aim, banks have to be continually vigilant by implementing enhanced safety measures that protect against safety threats from browsing the internet or engaging in on-line banking actions.
An Integrated Cyber Security Threat Management Framework For Online Banking Systems
Stakeholders are made conscious of hidden risks which may affect their very important usage and monetary transactions, enabling them to take required precautions and security controls to forestall risks and threats from realising. Risk management has constantly been a core perform in banking, with a primary focus on addressing profitability challenges. Conventional banking dangers, as categorized by 14, embody financial risks similar to credit score, liquidity, and earnings risks.
A distinctive mixture of offensive and defensive SOC companies allows you to conduct and develop your business with excessive security ranges. A Menace Model, Threat Model, and Meta Mannequin type the foundation of the framework. The Meta Model defines the complete framework as notated with ArchiMate modelling device in Fig. 2, with each Menace Model and Risk Model thought to be significant autonomous components. The diagram denotes realisation/influence relationship between elements by method of data construction and will be defined in particulars within the coming sections. Remodel your safety program with solutions from the biggest enterprise safety provider.
In Accordance to Security Journal, there are over 2,200 assaults every day which breaks down to almost 1 cyberattack each 39 seconds. The KuppingerCole information security platforms report provides steering and proposals to search out delicate information safety and governance merchandise that greatest meet clients’ wants. The convenience of online banking may be its downfall for a cyber-conscious client. Avoid logging into your on-line banking apps when you’re related to a public WiFi hotspot. You’re better off finishing these duties on a known network on a trusted pc. Whether you’re in an airport, library, or your favourite coffee shop, avoid doing any online banking or typing in your bank card data.

1 Applicability Of The Proposal And Comparison With Current Approaches
This could be addressed by adopting a standardized, systematic, and partially automated methodology that simplifies processes whereas maintaining rigour. PCI DSS is a set of safety requirements designed to protect customer information and payment data from unauthorized entry, use, or disclosure. Compliance with the PCI DSS is obligatory for any company that processes, shops, or transmits bank card data. By adhering to those requirements, corporations can ensure the integrity of their customer knowledge and shield it from cyber threats. As A Result Of of uncertainty around working remotely and the digital protection of businesses, cybercrime has drastically elevated by 600%.

Initial risk scenario identification and vulnerability evaluation may be enhanced by leveraging information on emerging menace tendencies particular to the monetary sector. Moreover, automating risk matrix calculations tailor-made to the context of OBS would simplify threat degree dedication across totally different users whereas maintaining standardization. Flaws could also be contained in security measures safeguarding information property and examples of particular vulnerabilities will be outlined in next part. Figure 3 illustrates an example of cascading relationships with potential flaws or assaults that allow attackers to additional infect or bypass subsequent controls. Developing a user-friendly yet efficient framework poses challenges, particularly in guaranteeing that tools are both accessible to smaller organizations and capable of delivering significant results. One major hurdle is balancing well timed decision-making in threat remedy with avoiding overly detailed analyses that will hinder actionable outcomes.
Spoofing is a form of cyberattack where criminals disguise their identity as a trusted and recognized source so as to https://www.dbfnetwork.info/finding-ways-to-keep-up-with-software/ steal confidential data or cash. Banks are underneath constant threat from spoofing assaults, which might have serious consequences for his or her clients and operations. Moreover, a man-in-the-middle attack is gaining momentum where a hacker intercepts communications between a buyer and the financial institution, in order to achieve access to non-public data, divert payments, or even launch a denial of service attack. As such, it is important that banks stay vigilant and take steps to guard themselves from these threats. While the framework introduces a quantity of advantages, there are areas for further refinement and enhancement to encourage broader adoption and ease of use. Automation tools can assist the framework’s implementation, enabling constant record-keeping and streamlining iterative processes.
AI brokers are infamous for deleting databases and directories, making it a small leap to imagine they trigger some havoc with unfettered entry to a bank account. One of the fears that executives have is when an AI agent with login access takes unauthorized steps, like spending cash or transferring funds around with out the explicit instructions of the account proprietor. There have even been situations where an AI agent known as the financial institution directly and took actions impartial of direct user command. Even although it wasn’t explicitly told to do this transaction, it thought-about it a vital step to perform the task assigned to it. Other appropriate risk evaluation methodologies can be utilized and customised within the framework, such because the OWASP Risk Ranking Methodology which estimates chance and impression levels on a three-level scale (low, medium and high).
In recent years, cybercrime has increased a lot that it’s already objectively thought-about the biggest threat to the financial sector. As hackers’ approaches and experience have improved, it’s becoming more difficult to repel attacks persistently. The unfortunate reality is that cyber security dangers are of rising concern for monetary institutions. Due to this fact, monetary establishments have innovated and accelerated the method to cyber safety to safeguard member property. To additional strengthen cybersecurity, adaptive authentication strategies have been proposed.
Commentaires récents